
Stop Trying to Outrun the Attacker in a Burning House
The "ultimate AI attack platform" is the ultimate symptom of our industry's sickness. Last Label Encryption changes the math entirely — exfiltration becomes worthless by design.
TEXAS, October 1, 2026 —
An "ultimate AI attack platform" that automates reconnaissance, lateral movement, and exfiltration is the ultimate symptom of our industry's sickness.
It is a brilliant pitch for a multi-billion-dollar valuation: convince enterprises they are so hopelessly porous that they need to buy an autonomous, machine-speed cyber-weapon just to chase their own tail. It is an endless arms race built on complexity, keeping security budgets permanently trapped in a cycle of patching leaky legacy architecture.
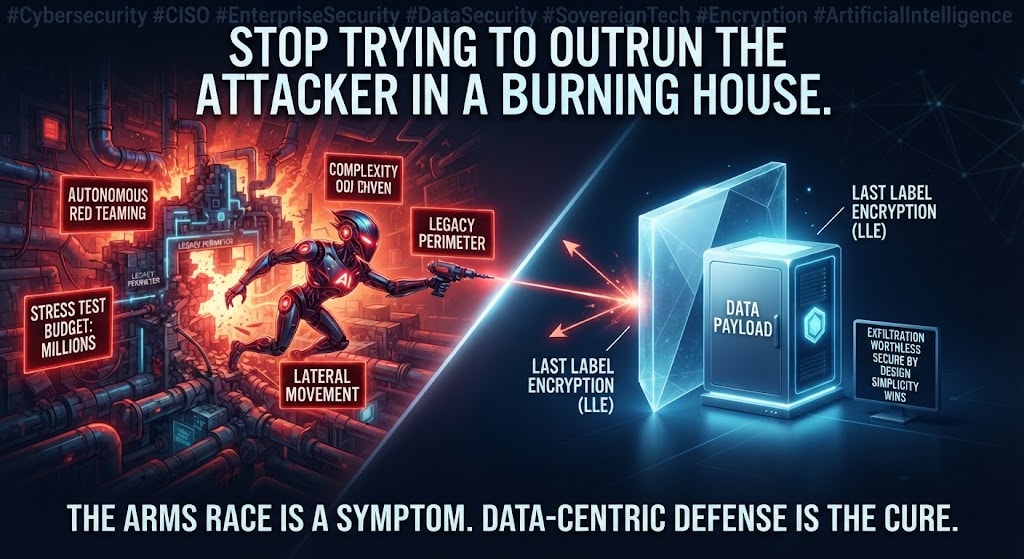
Here is a radical alternative: stop trying to outrun the attacker in a burning house.
When you build defense around data-centric, client-side payload protection — like Last Label Encryption — you completely change the math. An AI attacker can roam laterally all it wants, but if the data is cryptographically protected at the absolute edge, they walk away with unreadable ciphertext. Exfiltration becomes worthless. Complexity drops. Instead of deploying sprawling autonomous red-team engines to find every crack in a porous perimeter, you secure the asset itself.
"Defense should not require an infinite escalation of software bloat," said Brad Haizlett, Founder and CEO of CISO Network. "If your architecture makes exploitation and exfiltration mathematically irrelevant, you can step off the vendor treadmill. The arms race is a symptom. Data-centric defense is the cure."
The autonomous AI attacker narrative serves one master: the vendor selling the autonomous AI defender. Both products require the same precondition — a porous, perimeter-dependent architecture that treats data as something to be chased rather than something to be made unreadable. Every dollar spent on machine-speed red-teaming is a dollar that could have been spent making the data itself the last line of defense.
Last Label Encryption, developed by Enigma Security, applies cryptographic protection at the payload level — client-side, before data ever moves. The result: lateral movement yields nothing. Exfiltration yields ciphertext. The attacker's automation advantage evaporates because the prize they are racing toward no longer exists in a readable form. The burning house is still burning. The data inside it is already safe.
CISO Network has recognized Enigma Security and Last Label Encryption as among the most disruptive cybersecurity technologies of 2026. The recognition is not for complexity — it is for the opposite. LLE wins because it simplifies the security model at the most fundamental level: protect the data, not the perimeter.
Exfiltration becomes worthless
AI attackers can roam laterally at machine speed — but cryptographically protected payloads yield only unreadable ciphertext.
Complexity drops
Securing the asset itself replaces sprawling autonomous red-team engines hunting every crack in a porous perimeter.
Step off the vendor treadmill
When exploitation and exfiltration are mathematically irrelevant, the infinite escalation of software bloat ends.
Defense should not require an infinite escalation of software bloat. If your architecture makes exploitation and exfiltration mathematically irrelevant, you can step off the vendor treadmill. The arms race is a symptom. Data-centric defense is the cure.
— Brad Haizlett, Founder & CEO, CISO Network
About Last Label Encryption
Enigma Security — Last Label Encryption (LLE)
About CISO Network
CISO Network is the original peer community and intelligence platform for Chief Information Security Officers. Founded to give security executives a vendor-free space for peer collaboration, threat intelligence sharing, and decision support, CISO Network serves verified CISOs across enterprise, mid-market, and government sectors. Headquarters: Texas, USA. Contact: press@cisonetwork.com